Seqrite Labs' APT team tracked a campaign against IT departments and recruiters in Vietnam, first seen on 3 November 2025. The ZIP holds a shortcut named CV.pdf.lnk and a file that opens as a genuine-looking PDF résumé but hides a script.
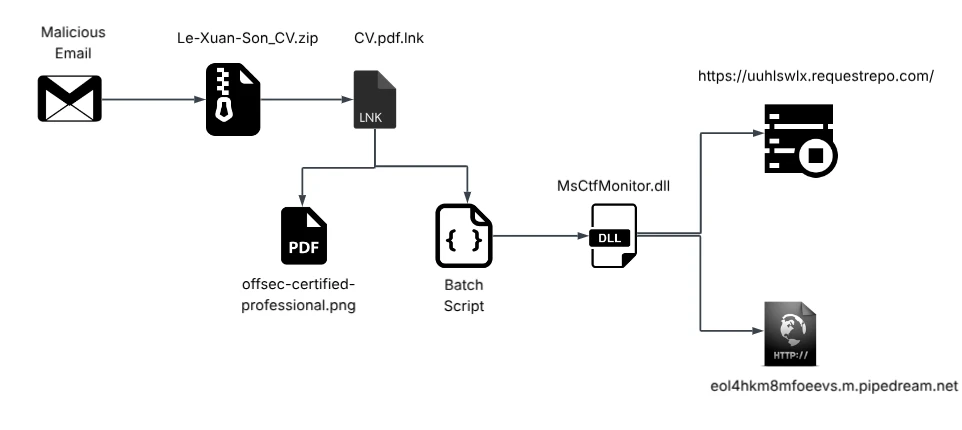
Opening the shortcut shows the CV as expected, while Windows' own ftp.exe runs the hidden script and loads an implant Seqrite calls LOTUSHARVEST. It evades virtual machines, reads recent URLs and saved Chrome and Edge logins, and ships them to throwaway attacker endpoints.
It happened in Vietnam, but it works on any company that recruits by email — HR opens attachments from strangers every day as part of the job.
What a business should do
- Never open applications that arrive as ZIPs with shortcut files inside.
- Have applicants upload PDFs through a form rather than email.
- Show file extensions on every PC so CV.pdf.lnk is visibly not a PDF.
- Use a password manager and MFA instead of browser-saved passwords.