Seqrite XDRSignals from every layer, as one incident
For organisations with several sites or systems — endpoint, network, email, cloud — that need the whole attack on one screen instead of reading logs tool by tool.
See everything, respond from one place
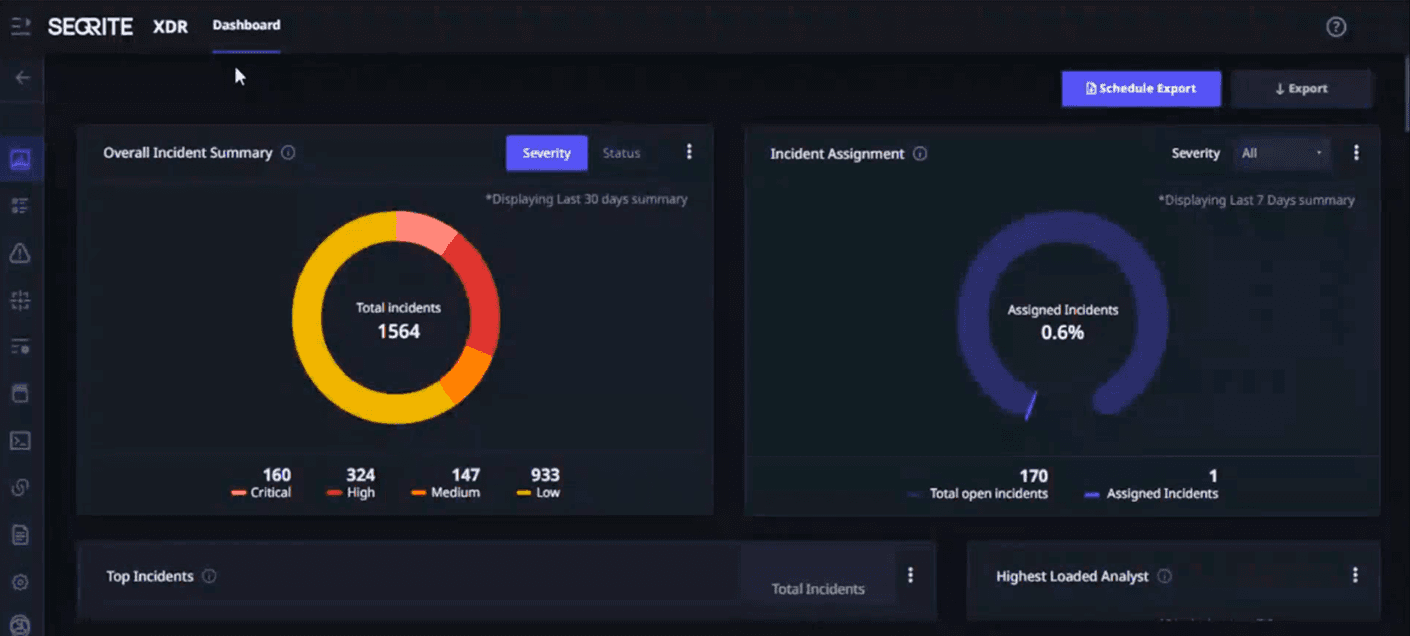
Correlate across layers
GoDeep.AI ties signals from many sources together to confirm high-confidence incidents and cut duplicate alerts.
- Cross-layer correlation
- MITRE ATT&CK rules
- One place for every alert
Investigate faster with AI
SIA, the AI analyst, answers questions about incidents and alerts; the workbench pins down source and activity.
- SIA — AI security analyst
- Investigative workbench
- Threat hunting across endpoints
Respond with playbooks
Automatic or manual response playbooks through built-in connectors, with an audit log for reviewers.
- Playbook automation
- Built-in connectors
- Audit log
What XDR does
- SIAAI security analyst
- Intelligent DetectionMITRE and multi-system rules
- Investigative WorkbenchAlerts grouped into incidents
- Threat HuntingIOC hunting across endpoints
- Playbook AutomationAutomated response
- GoDeep.AI CorrelationCross-layer confirmation
- Unified ConsoleEverything in one place
- Audit LogReady for review
- Includes EDREverything in EDR
How Seqrite XDR is priced
Priced on endpoint count and the systems connected. The quote includes the genuine licence, updates for the full term, and Thai support. If a cheaper edition such as EDR is enough, that is what we'll propose.
Get a quote — answered within one business day →What we ask to quote it
- 01Endpoint count and number of sites
- 02Systems to connect, e.g. firewall, email, Microsoft 365, cloud
- 03Contract term, 1–3 years
- 04Whether you want our team to set up response playbooks
XDR is the step after EDR
- — Anti-ransomware
- — Web + device control
- — Patch management
- — Thai support
- — Everything in EPP
- — Root cause analysis
- — Auto-response & rollback
- — Thai support
- — Everything in EDR
- — Cross-layer correlation
- — Playbook automation
- — SIA AI security analyst
Moved in batches to minimise unprotected time
We remove the old antivirus, set policy, and move machines over in batches, at times that disrupt least — agreed with the quote.
See the deployment service →- 01Survey what you run todayCount devices, operating systems and the antivirus in place.
- 02Set policy to how you workNothing left on untuned defaults.
- 03Move in batchesOld agent out, Seqrite in, back to back, batch by batch.
- 04Hand over and look after itConsole walkthrough, and a reminder before the licence expires.
Before you start a trial
How long is the trial, and does it cost anything?
30 days, no cost and no commitment. We email the trial licence and install steps to the address you give us.
How is XDR different from EDR?
EDR looks at endpoints. XDR brings in signals from several layers — endpoint, network, email, cloud — and ties them into one incident. It suits organisations with several sites or systems.
Does an SME need XDR?
Not always — many start with EPP or EPP + EDR and that's enough. We size it from your devices and systems, and if a cheaper edition is enough, we'll tell you.
Is support available in Thai?
Yes. Tickets land with engineers in Thailand, by phone, email and LINE, Mon–Fri 09:00–18:00. Where the manufacturer is needed, we escalate through the partner channel directly.
Why aren't prices on the website?
Pricing follows device count and a 1–3 year licence term. Send the number of devices and we'll quote within one business day — and if a cheaper edition is enough, we'll say so.
The Official Seqrite Distributor in Thailand
Cybernex Group Co., Ltd. sells, deploys and supports Seqrite with a Thai engineering team. Seqrite is a product of Quick Heal Technologies Ltd.; every licence is genuine, issued by the brand owner.
- Company certificate
- VAT registration (P.P.20)
- Full tax invoice
- PO accepted
- Vendor registration
Cybernex Group Co., Ltd.
Try Seqrite XDR for 30 days
30 days, no cost, no commitment. We'll send a trial licence and install steps to the email you give us.